Production Investigation Kit
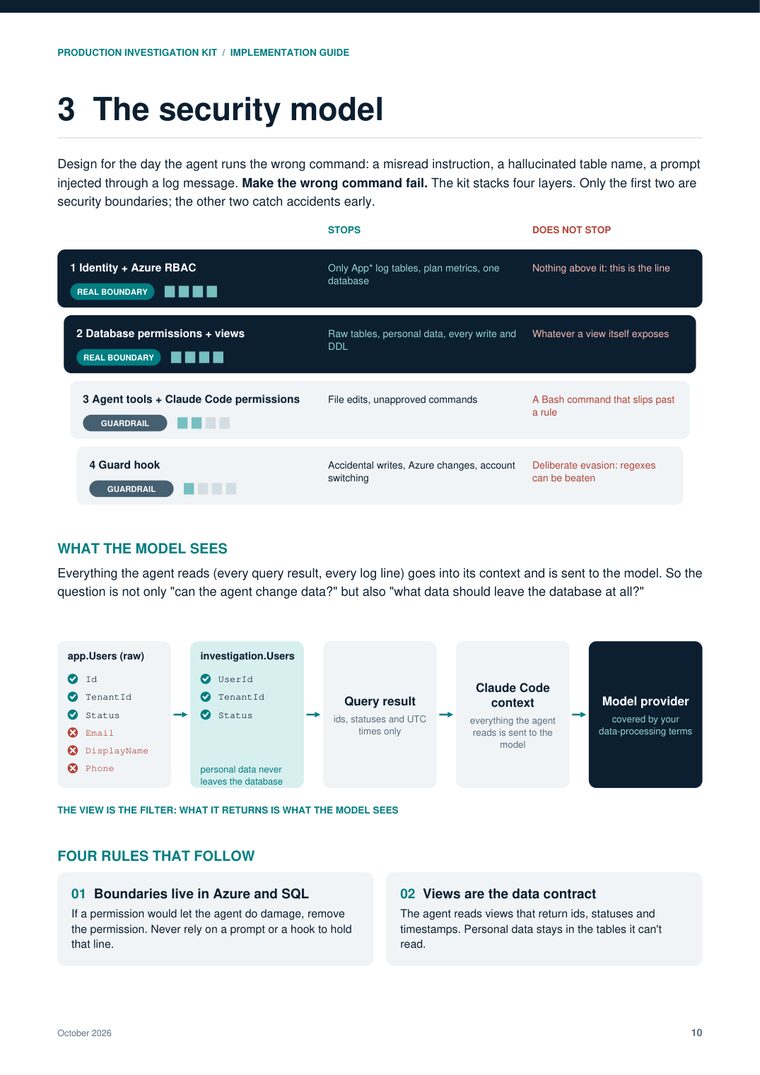
Evidence-first production investigations with Claude Code, on top of scoped, least-privilege Azure access. The security design is part of the resource: an investigator-only identity, restricted SQL views, auditing and separation of duties, with agent-side guardrails layered on top.
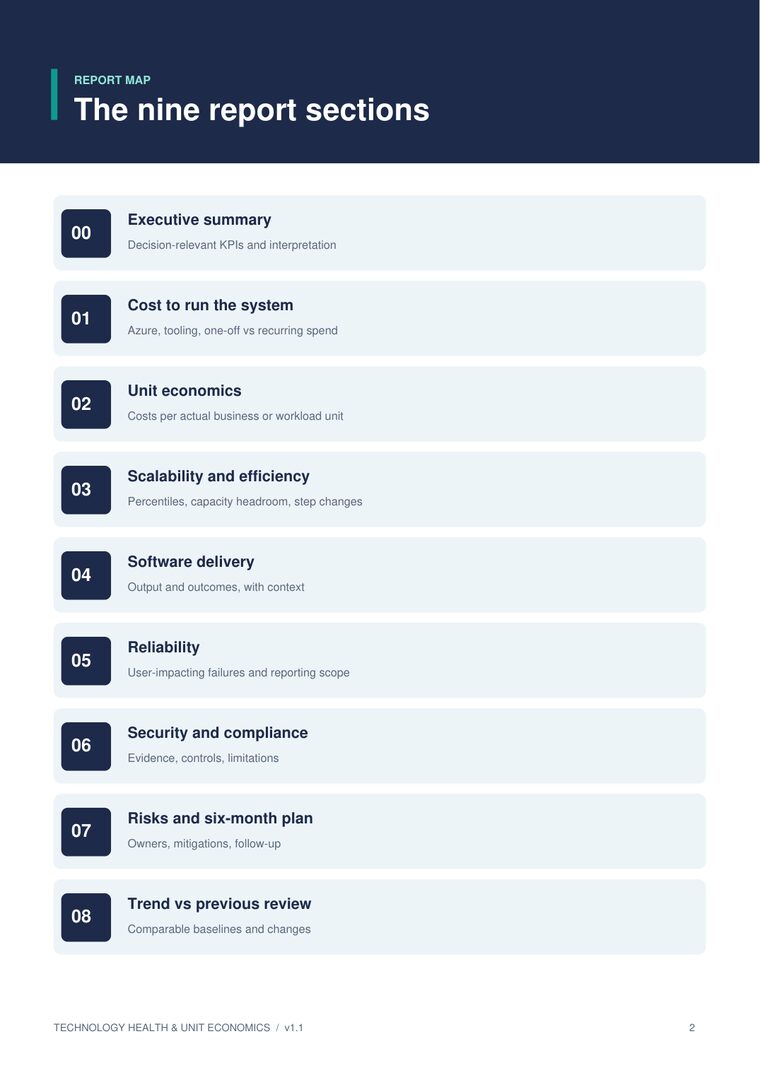
- Investigator sub-agent plus skills for the investigation procedure, SQL queries and KQL / Log Analytics queries
- Azure identity, group and role setup, investigation views and read-only database access
- Auditing, and a separation between investigator access and audit-log access
- A guard hook that blocks write operations, Azure changes and account switching
- PowerShell and Bash setup scripts, prerequisite checks, guard tests and a verification checklist
- Worked examples and an evidence-linked report structure
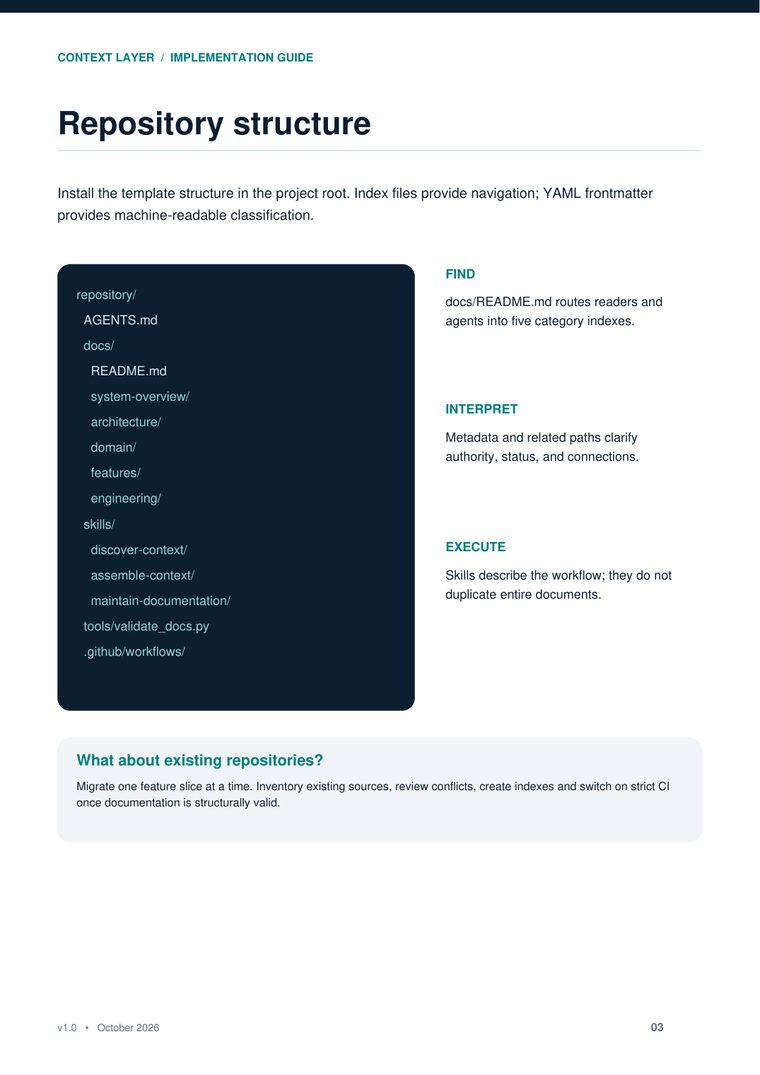
Production_Investigation_Kit/
├── .claude/
│   ├── agents/investigator.md
│   ├── hooks/investigation_guard.py
│   └── skills/  investigate · query-sql · query-kql
├── azure/       01-create-groups … 07-verify-access
├── GUIDES/      01_WHAT_YOU_WILL_BUILD … 06_CHECKLIST
├── tools/       check_prereqs · scan_for_identifiers · test_guard
└── Production_Investigation_Kit_Guide.pdf
Assumes Claude Code, Azure App Service, Azure SQL and Application Insights / Log Analytics. It documents an opinionated, working setup: adapt it, test it in a sandbox first, and never run it directly against production.
“I especially like that it goes beyond the concepts and covers the actual implementation, from setting up least-privilege access and auditing to integrating Claude Code and adapting the workflow to a real system. This kind of practical, security-conscious approach to AI-assisted engineering is exactly what I'd like to learn more about.”
Amirhosein, .NET Developer